Related Topics:
Network Security Solutions Enterprise-
Enterprise Network Planning Layer 3 Core Switches
The L3 switch is ideal for service provider edge aggregation, enterprise wiring closets, data center aggregation, and network core deployment. A core switch is a high-capacity, high-performance Layer 3 switch positioned at the physical backbone of an enterprise network. Engineered to aggregate massive volumes of data from distribution switches, it provides ultra-low latency and maximum throughput to ensure uninterrupted routing and packet. A scalable enterprise switching architecture, or enterprise switching architecture, consists of three functional layers: 1. They provide high performance, resilient stacking, wire speed. What Are Layer 3 Switch Examples and How Do They Benefit Enterprise Networks? A Layer 3 switch combines switching and routing functions to efficiently manage traffic within and between VLANs on a LAN. Layer 2 switches forward information based only on the MAC address (the Layer 2 frame address).
[PDF Version]
-
Use network security equipment correctly and effectively
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Build a vulnerability management program. We'll explore how powerful solutions, like those from industry leaders Cisco and Meraki, can help you build secure, seamless. This guide provides a detailed roundup of the most critical network security best practices for modern enterprises.
-
Essential Network Security Equipment
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. Unlike firewalls, which prevent access, IDS works by detecting and alerting administrators to potential security incidents. They help to. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. ManageEngine Vulnerability Manager Plus Best for vulnerability and patch management in Windows environments 2.
-
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]
-
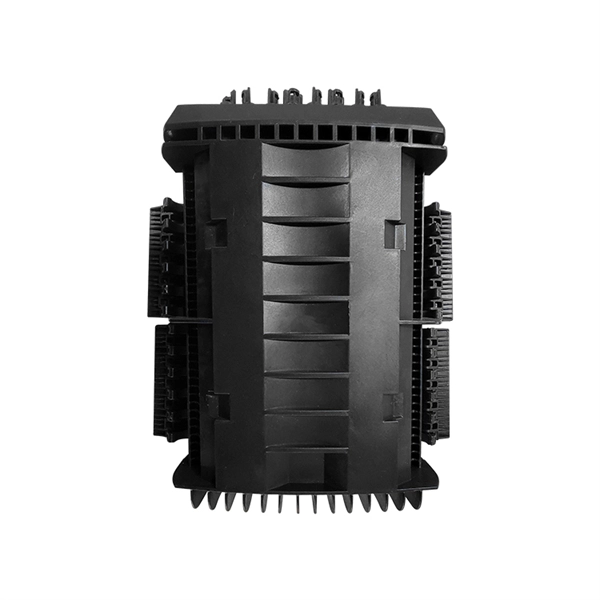
Office Network Security Equipment Configuration Standards
For improved network security, the Trusted Computing Group (TCG) is developing standards/guidance that specifically addresses the security of networking equipment. The TCG Guidance for Securing Network Equipment Preview Synopsis provides a summary of the ongoing. Establish, implement, and actively manage (track, report on, correct) the security configuration of network infrastructure devices using a rigorous configuration management and change control process in order to prevent attackers from exploiting vulnerable services and settings. Why is this CIS. This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U. NIST is responsible for developing information security standards and. Securing network devices is essential for preventing unauthorized access and maintaining network integrity. By enforcing standardized security policies and. This article provides best practices for each of these aspects, ensuring a robust and efficient office network setup. Steps for Provisioning Servers 3.
[PDF Version]
-
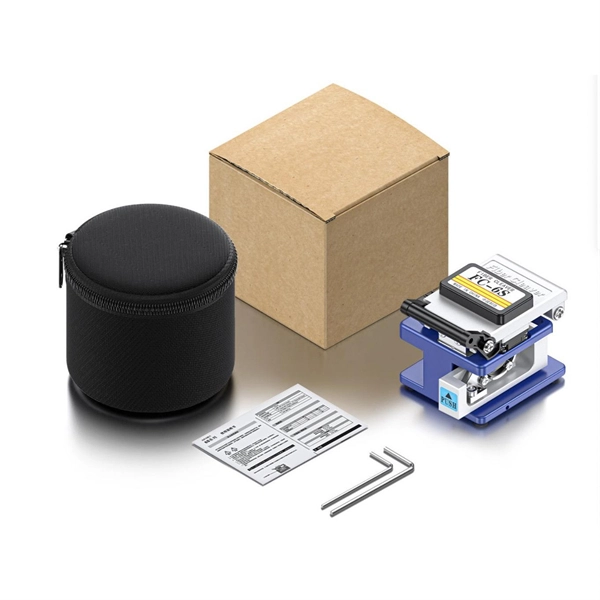
Denmark Network Cable and Fiber Optic Cable Manufacturer
The leading Fiber Optic Cable Manufacturers in Denmark are listed in this directory. Identify and compare relevant B2B manufacturers, suppliers and retailers Fiberby is a specialized service provider offering high-speed fiber optic internet solutions for housing networks in the Copenhagen area. Until the electrician do us part. Nexans Hybrid Cable EXQ/GRHAL Nexans Hybrid Cable EXQ/GRHAL combines power and fiber in a shared sheath –. Single & Multi Loose Tube Micro Fiber Optic Cables with Single Mode Optical Fiber G-657A / G-652D. GM Group is a supplier in the industry of high-technology pipes, cable pipes and systems for energy and telecommunications. You can narrow down the list of manufacturers based on their location and capabilities, browse their product catalogs, view their profiles, and send inquiries. Explore this list as a starting point and.
[PDF Version]
-
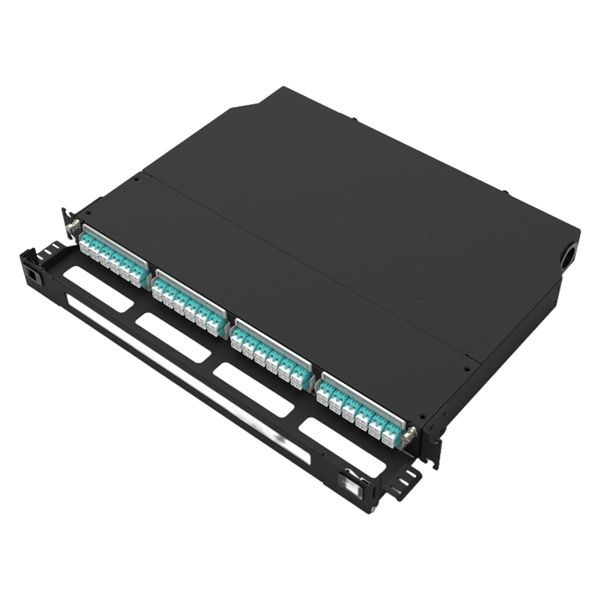
Network Rack Temperature Control Solution
Small racks use compact in-row coolers or passive rear-door heat exchangers. The Liebert® DCD chilled water-based cooling family was designed specifically for high heat density applications where the challenges of reducing energy consumption and increasing processing capabilities are the top priority for data. 1 Impact of Heat on Server Lifespan and Performance Electronic. In our Lehmann IT Shop, you'll find heating and cooling solutions to enhance the performance and protection of your electronic devices. Here's what we offer: Heating Fans for Extreme Conditions Ideal for outdoor use and demanding industrial applications. Implementing effective rack cooling ensures: Equipment Longevity: Protects sensitive components from thermal stress. Operational Reliability: Minimizes unexpected shutdowns. Compliance: Meets industry standards like ASHRAE and. From understanding the unique cooling needs of high-density racks to exploring advanced techniques like liquid cooling and airflow management, this guide dives into practical solutions and emerging trends. Whether you're managing a small server room or a sprawling data center, the right cooling.
[PDF Version]
-
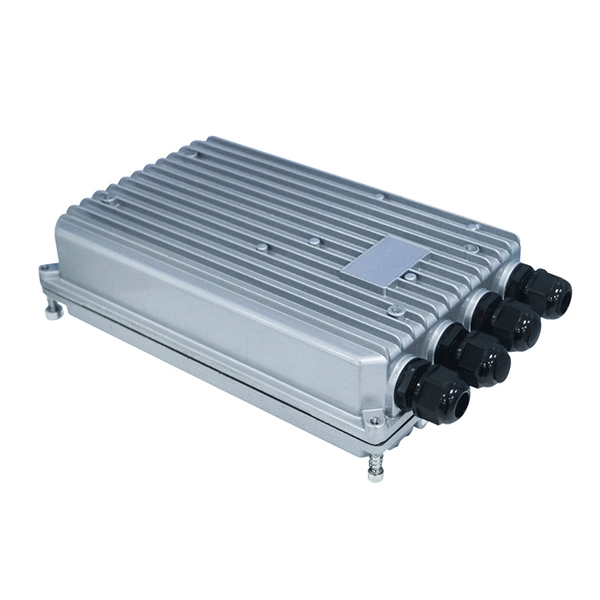
Parameters of Professional Network Cabinets
The right Network Cabinet size is determined by three key factors: total rack units (U) required, equipment depth, and future expansion capacity. In most business environments, choosing a cabinet with at least 20–30% extra rack space prevents overcrowding and extends system. A Network Cabinet, often interchangeably called a server rack, is a physical frame or enclosure designed to house and organize various types of network hardware and accessories. This includes routers, switches, servers, patch panels, and other networking equipment. In fact, these cabinets measure around 600–800 mm in depth. A well-selected cabinet not only optimizes space and facilitates cable management but also ensures operational continuity and the integrity of the equipment. This research covers the global server and network cabinet market, focusing on. In general, smaller or wall-mount racks are suitable for home or office rack installation; while 4-post racks or enclosed server racks are greater for data centers or server rooms.
[PDF Version]
-
Network cable reservation inside the network rack
Pro Tip: Reserve the left side of your rack for power cables and the right for network cables to prevent interference and simplify troubleshooting. Learn Cat6A requirements for Wi-Fi 7, PoE++ thermal management, SFP+ uplinks, and proper installation techniques for 10Gbps infrastructure. A well-documented infrastructure is easier to add onto, upgrade, change and maintain. Bundling. Enables 40 kW+ per rack densities with structured routing, reducing space needs by 30%. Reduces maintenance time by 50% with tools like trays and. Network Rack Cable Management refers to the systematic process of planning, laying out, securing and labeling data cables and power cables inside the cabinet. These elements form the foundation of a structured, reliable installation: Cable Tray Systems They provide the main pathways to support and distribute large bundles of network and power. Take note of your servers, switches, and other devices, power distribution units (PDUs) locations, and available rack space to plan clean cable paths that avoid clutter, maintain airflow, and simplify maintenance.
[PDF Version]
-
High-precision battery cabinets are used for campus network applications
Telecom battery cabinets are specialized enclosures housing backup batteries that provide uninterrupted power to telecommunications infrastructure during outages. They ensure network reliability by storing energy, regulating voltage, and supporting critical systems like cell towers. Factory assembled with LFP (Lithium-Iron-Phosphate) battery modules and Vertiv's internally-powered battery management system, Vertiv EnergyCore cabinets are available globally and are qualified for use with most current and legacy three-phase Vertiv™ uninterruptible power supply (UPS) systems. Every battery's performance and lifespan is determined during the formation process, and battery test and formation equipment is designed for a specific application. Low-current equipment uses converters with integrated switching field-effect transistors (FETs) to charge and discharge.
[PDF Version]
-
Fiber Module Network Port Test
The simplest way to test an SFP transceiver is with the FiberLert™ live fiber detector, which lights up and beeps when placed in front of an active fiber or port. There are no specific requirements for this document. To perform a loopback test on SFP ports in a FortiGate firewall, the goal is to verify that the port is functioning correctly (both transmitting and receiving data). An optical. This Applications Engineering Note (AEN 135) explains and recommends standard measurement methods for characterizing optical fiber system performance. This note also provides background information on system link configurations, test equipment and system component considerations that influence. In fiber optic networks, optical transceivers such as SFP, SFP+, QSFP28, and QSFP-DD play a vital role in converting electrical signals into optical signals and vice versa. Testing these modules ensures performance, compatibility, and long-term reliability in bandwidth-intensive environments like.
[PDF Version]