Related Topics:
Your Guide Market Access-
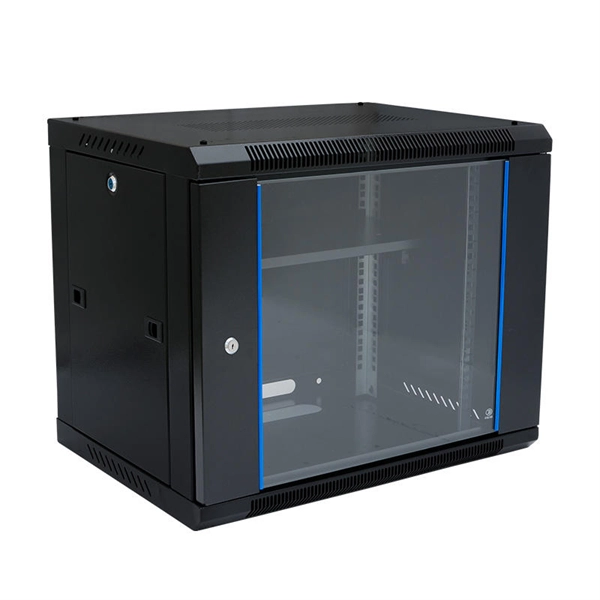
Function of the guide rail in the distribution box
Guide rails, also known as linear guides, are mechanical elements designed to ensure smooth, precise and controlled linear movement of objects. They generally consist of two main components: the rail itself and a sliding carriage that moves along the rail. The guide rail slot seat is provided with several. Busbars: These are solid strips of copper or aluminum that transfer electricity from the main source to the individual circuits inside the box. It integrates power distribution, protection, and monitoring capabilities, and is responsible for distributing power to entire commercial or residential. The distribution box (DB box) helps safely and efficiently distribute electrical power.
-
Does the access switch need a power supply
A typical access control setup includes a low voltage wire (e., 24V), as well as backup power supplies for locks and access system. This is because they want to make an informed decision and select the models that best fit their project requirements. Here, we have prepared a detailed. Does your access control system have a built-in power supply, or do I need to purchase a separate one? Does your access control system have a built-in power supply, or do I need to purchase a separate one? Our controllers support PoE or any regulated power supply between 12-24V, but power supplies. Before buying these products I checked the specs and it would appear the POE switch should power the AP, but it does not? See specs and device info below. I then plugged in the AP to the switch, and the AP did not power. To get the best PoE performance, you should provide enough PoE power to exceed the maximum amount of power that is needed by all the PDs that are being used. Additionally, the access layer switch is more adept at interacting with endpoints from a security perspective.
[PDF Version]
-

Optical Access Device epon
EPON, or Ethernet Passive Optical Network, stands as a passive optical network technology developed by IEEE based on the 802. Similar to GPON, EPON presents an effective fiber access solution with a coverage radius extending up to 20 kilometers. It uses only optical fibers to transmit data, voice, and video services. This guide dives deep into EPON technology, its benefits over alternatives like GPON, and the critical role of optical modules. The PON technology includes: · Ethernet PON (EPON), a passive optical network based on Ethernet, is. EPON modules play a pivotal role in facilitating fast and reliable data transmission over fiber optic networks, offering enhanced bandwidth capabilities and improved network efficiency.
-
Aggregation switch access optical module
A fiber optic aggregation switch is a high-capacity network device designed to integrate and manage multiple fiber optic connections from access layer switches into fewer and faster uplink connections to the core network. It also enables easy expansion by simply adding more fiber or network switches. Long-distance installations often require fiber optic cables to connect different sites because of. The Xingmai Passive Ethernet Network (PEN) is an all-optical campus network solution based on the passive technology. Faster replacement and priority support, covered for 5 years. High-performance 10G SFP modules for optimal connectivity. At the heart of a point-to-multi-point or passive optical network (PON) is the optical line terminal (OLT). The access layer switch is the equipment of the switching. An aggregation switch is a network device that consolidates traffic from multiple access switches, wireless access points, or other edge devices and forwards it to core switches or routers.
[PDF Version]
-
Which layer device is typically used in an access switch
Access switches are layer 2 switches that operate at OSI model layer 2 (data link layer). It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic. The access layer plays a critical role in connecting end devices—such as computers, printers, IP phones, and wireless access points—to the rest of the enterprise network. This guide will demystify these roles and help you understand their. The core switch is a high-end device that is used to connect all the access switches. The access layer is supposed to make it easier for end devices to stay connected.
-
Can Huawei s core switches manage access points APs
In addition, core switches are configured with the native AC function to manage APs and transmit wireless service traffic on the entire network, implementing wired and wireless convergence. This document provides the use precautions of the product, including licenses, software versions, feature dependencies, limitation, and involved network elements. 1 Configuration Limitations for AP Management 7. It is usually deployed at the aggregation layer to configure and manage access points (APs) in batches. It can be used to construct large- and medium-sized campus networks, enterprise office networks, wireless metropolitan area. Huawei's AirEngine Enterprise Access Points (APs) combine next-generation Wi-Fi 6 / 6E / 7 technologies with AI-driven optimization and centralized cloud management, creating high-performance, scalable wireless networks for businesses of all sizes. In the past, companies relied heavily on wired.
[PDF Version]
-
Access Layer Switch VLAN and MAC Binding
The MAC-based VLAN feature allows incoming untagged packets to be assigned to a VLAN and in that way, you can classify traffic based on the source MAC address of the packet. You can use VLAN maps to filter traffic between devices in the same VLAN. Unsupported protocols are. VLANs can be assigned based on interfaces, MAC addresses, IP subnets, protocols, and policies (MAC addresses, IP addresses, and interfaces). Table 5-2 compares different VLAN assignment modes. A network administrator preconfigures a PVID for each interface on. In this article, we will dive into switching basics, focusing specifically on VLANs (Virtual Local Area Networks) and MAC address tables, two critical components in managing traffic within local networks. It is required that Laptop A can only access Server A and Laptop B can only access Server B, no matter which meeting room the laptops are being used in. VLAN access-map configuration is very similar to the Route-map configuration.
[PDF Version]
-
RS2352 Access Switch
Equipped with 48 Gigabit Ethernet ports and 4 SFP+ ports, this switch offers intelligent management and numerous security features. Orchestrated from the LANCOM Management Cloud, it is configured dynamically, automatically, and efficiently by SD-LAN. LANCOM fully managed access switches are the secure and powerful networking foundation in all industries and application scenarios. 5G, 10G and multi-Gigabit Ethernet, they are immediately ready for connecting any network components – including high-performance Wi-Fi 7. This 52-port switch gets professional networks ready for the future: Along with the wide range of power management functions for energy efficiency, the LANCOM GS-2352 supports both current Internet protocols IPv4 and IPv6. The implementation of dual-stack enables the switch to operate in pure IPv4, pure IPv6, or in mixed networks.
[PDF Version]
-

Access Switches Cascaded with Switches
Switch cascading is a traditional method to interconnect multiple Ethernet switches. Among the various topologies, daisy chain and star are the most. Thus, multiple Ethernet switches are connected together using different techniques, primarily switch cascading, switch stacking, and switch clustering. I am following this diagram: I will be using CISCO SG500-28 Managed Switch as my main switch, where another switch CISCO SG250-18 Managed Switch will tap in. Connections: Set up a switch cascade by simply connecting the uplink port of one switch to. Cascading switches refers to the process of connecting multiple switches together in a series, effectively expanding the network's capacity and reach. The below content will show you three methods. Multiple switches can be cascaded in various ways as needed. In a larger local area network such as a campus network (campus network).
[PDF Version]
-
Port down after VLAN segmentation on access layer switch
Symptom: The switchport is shutting down or not passing traffic after connecting a device. Cause: Port security may be misconfigured, leading to violations that cause the port to go into an error-disabled state. Please rate and mark as an accepted solution if you have found any of the information provided useful. This then could assist others on these forums to find a valuable answer and broadens the. An SVI stuck in up/down means something is wrong with the underlying VLAN — no active ports, a deleted VLAN, or STP blocking every path. Here is how to diagnose and fix every cause. You configure an SVI, assign an IP address, type no shutdown, and expect it to come up. Instead, show ip interface. Network segmentation is crucial for security, performance, and efficient network management., computers, printers) connect to a switch.
[PDF Version]
-
Cisco Access Layer Switch Permissions
Cisco IOS devices use privilege levels for more granular security and Role-Based Access Control (RBAC) in addition to usernames and passwords. To access Cisco Feature Navigator, go to http://www. By default: Each command in IOS is assigned a default. We can configure different command access based on priviledge level of user logged in. Level 15. In this guide, we'll break down everything you need to know about Cisco ACLs: from the basics of standard and extended lists, to advanced configuration examples, to real-world troubleshooting tips that save hours of downtime. If the startup configuration has a convoluted type 9 secret, and you downgrade to a release prior to Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device.